Repository navigation
Password step 400 — Auth0 tenant migrated to new React Universal Login (ULP 1.125 / react-components 1.202, custom af-form) #295
Description

- Integration v0.5.3 (latest), HA 2026.7.4, Docker Container install.
- Symptom: identifier step succeeds (302 → /u/login/password), but the password POST https://auth.ecobee.com/u/login/password returns HTTP 400 with no data-error-code. Credentials are correct.
- This is a genuine Auth0 response, not a bot/WAF block or rate-limit: headers include X-Auth0-RequestId, X-Auth0-L, X-RateLimit-Remaining: 422.
- The 400 body is Auth0's new React ULP, not the classic form:
- custom-form markup: af-custom-form-container / af-form (Auth0 Forms)
- Conclusion: the tenant switched to the new React Universal Login with custom Forms; the direct POST state/username/password/action=default to /u/login/password is no longer accepted. The scripted _password_step / _post_login_form flow needs to be reworked for the new ULP.
Activity
binarydev commentedon Aug 1, 2026
Hey, thanks for the bug report! Unfortunately I can't seem to recreate your issue. Can you please try upgrading to v0.5.4 that was just released with an unrelated auth fix, and try again?
hildebrau commentedon Aug 5, 2026
I'm hitting the same thing.. when upgraded to 0.5.3 as well as 0.5.4, I hit reconfigure and paste in my Generac password
It says: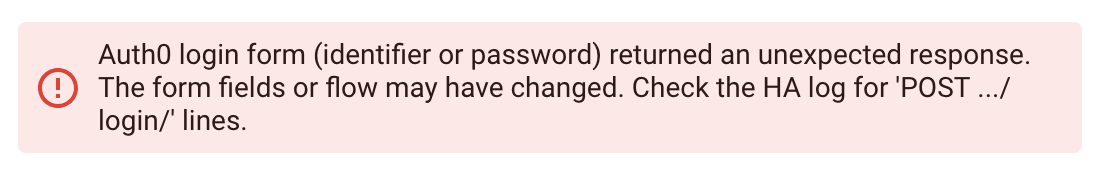
2026-08-04 20:13:58.153 WARNING (MainThread) [custom_components.generac.auth] Generac auth: step=authorize -> 302 loc=/u/login/identifier?state=REDACTED set-cookie-count=4 jar-after=['auth0', 'auth0_compat', 'did', 'did_compat'] 2026-08-04 20:13:58.231 WARNING (MainThread) [custom_components.generac.auth] Generac auth: step=identifier -> loc=/u/login/password?state=REDACTED 2026-08-04 20:13:58.441 WARNING (MainThread) [custom_components.generac.auth] POST https://auth.ecobee.com/u/login/password -> 400; auth0 error code=None 2026-08-04 20:13:58.442 ERROR (MainThread) [custom_components.generac] Login flow failed: step=login_form url=https://auth.ecobee.com/u/login/password status=400 no_code body='\n\n\n\n\n\n\n\n\n\n\n\n<!DOCTYPE html>\n<html lang=\'en\'>\n<head>\n <meta charset="utf-8">\n <meta http-equiv="X-UA-Compatible" content="IE=edge">\n <meta name="viewport" content="width=device-width, init' Traceback (most recent call last): File "/config/custom_components/generac/config_flow.py", line 130, in _try_login auth = await GeneracAuth.login(session, email, password) ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^ File "/config/custom_components/generac/auth.py", line 890, in login return await flow.start() ^^^^^^^^^^^^^^^^^^ File "/config/custom_components/generac/auth.py", line 668, in start resume_state = await _password_step( ^^^^^^^^^^^^^^^^^^^^^ self._login_session, pw_state, self._email, self._password ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^ ) ^ File "/config/custom_components/generac/auth.py", line 397, in _password_step loc = await _post_login_form(session, PASSWORD_URL, state, form) ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^ File "/config/custom_components/generac/auth.py", line 320, in _post_login_form raise RuntimeError( f"step=login_form url={url} status={resp.status} no_code body={text[:200]!r}" ) RuntimeError: step=login_form url=https://auth.ecobee.com/u/login/password status=400 no_code body='\n\n\n\n\n\n\n\n\n\n\n\n<!DOCTYPE html>\n<html lang=\'en\'>\n<head>\n <meta charset="utf-8">\n <meta http-equiv="X-UA-Compatible" content="IE=edge">\n <meta name="viewport" content="width=device-width, init'hildebrau commentedon Aug 5, 2026
Oh.. it seems Generac changed some things on their end since I last used their web app..
https://app.mobilelinkgen.com now redirects to https://auth.ecobee.com (as we see in the HA log).
That site says:
⚠ We updated our security on April 21, 2026. If you haven't reset your password since then, you'll need to do that before logging in. Use the "Forgot password?" link below.
So, I used Forgot password.. they send a PIN to your email for MFA.. filled that in, changed my password, and then logged in to find a EULA I had to agree to. It probably says not to use HA against their site.. dunno, didn't read it.
But then I went back and setup the HACS integration and it worked. I did delete the previous integration prior to figuring this out, though. Hopefully that step wasn't necessary.
markwilke commentedon Oct 24, 2026
Adding another data point that matches this issue exactly, with the credential
variable fully closed:
Environment
(they sit between the v0.5.1-era and v0.5.3/v0.5.4 layouts), so I am not
claiming a specific version; other reporters here have confirmed the identical
failure on both v0.5.3 and the latest v0.5.4.
What the logs show — two separate failures, decomposed
POST /u/login/identifier -> 400, auth0_code=invalid-email-format.That did not repeat once the address was re-entered carefully by hand
(the integration passes the email verbatim, with no strip/lower, so this
half appears to have been an input artifact, not an account property).
to
/u/login/password— and then failed at the password step:Login flow failed: step=login_form url=https://auth.ecobee.com/u/login/password status=400 no_codewith the response body being a full HTML page and no
data-error-codeanywhere in it. That is word-for-word the same shape reported above.
Credential verification (done after the failures)
current login: a fresh logout/login in the Mobile Link app, including 2FA,
succeeded. So the password is proven good on the current login flow.
ever produced — consistent with the new React Universal Login not rendering
the classic
data-error-codeattributes the integration parses.Happy to provide longer log excerpts if useful — noting the integration only
logs the first ~200 characters of the response body (blank lines + doctype),
so React ULP markers in the returned page can't be confirmed from the log alone.
Merge pull request #310 from binarydev/fix/issue-295-auth0-password-400
binarydev commentedon Oct 25, 2026
@markwilke this should now be properly handled with the latest v0.5.5 release
fix(auth): handle Auth0 password 400 without error code and strip ema…